-
Tweets4K
-
Followers14K
-
Following6
-
Likes968
All the details including the slides are now available at quentinkaiser.be/security/2026/…
My presentation at Hexacon is done ! Time for public disclosure. Pictured below: remote unauthenticated code execution over-the-air (including the shell) on Proximus BBOX 3V+
Yes my passcode is really 555555


Exciting work from @willzhou97 (Fellow, now full time!) and @bucketofkets on the Frontier Red Team. One of the cool parts of the job is seeing a future world early. We think this one is ~pretty underpriced. "We should aim to harden our systems to make it difficult for such replicators to spread, but also prepare to deal with a world where they are here to stay."
Anthropic's Frontier Red Team believes small AI models may now be months away from being capable of self replicating without access to a datacenter. Quoting from the blog: 'The capabilities that make AI models generally powerful coding agents also generalize to cyber tasks,


Very excited to share details on the bugs used in our full chain Chrome exploit! We used three bugs (V8 corruption, V8 sandbox escape, and renderer sandbox escape via Crashpad). The third bug is my favorite!


📚 Slide decks from OB1 2025 & 2026 are live! Catch up on talks you missed, revisit top sessions, or dive into the technical breakdowns. Most slides are up on GitHub: 👉🏻 github.com/star-sg/OBO Huge thanks to all our speakers, sponsors, activity partners, and attendees!

Agenda for OffensiveCon Tokyo 2026 is live! Explore the talks and plan your schedule now: offensivecon.jp/agenda/2026.ht… #OffensiveCon #Tokyo

Honestly impressed with Claude Opus 5.5 on this one.

We made an anime about SBOMs (with a lot of help from @claudeai). Then shipped v0.3.0 🎉 CBOMs now get checked against CNSA 2.0 + post-quantum rules, and if sbom-tools can't tell what an algorithm is. github.com/sbom-tool/sbom…

The Phrack 73 prophile of @halvarflake A must-read from one of the legends of vulnerability research. archives.phrack.org/dl/73/halvar-f…


To secure open-source software, we’re launching OSS Scanner. We’ll use our frontier models to periodically scan opted-in open-source projects for vulnerabilities, at no cost. Our reports will provide a proof-of-concept, explanation, and suggested fix. anthropic.com/research/launc…
We’re launching the Anthropic Cyber Mission, a new effort to secure critical infrastructure and open-source software. anthropic.com/news/anthropic…

@kmad @matthew_pines I think we might lose public key cryptography.
"not accepting attack surface in the design phase" is the *biggest* leverage we have, and it's ridiculous how rarely this is done in reality.
Agree on verification, but I'd push it further. Memory safety is a symptom, not the cause. We got here because of design decisions and trade-offs we made all along, and you can see it in pretty much every recent Linux kernel disclosure. Throwing more tokens at the attack surface
We’re expanding our Cyber Verification Program to give security professionals broader access to our most capable models. Through this program, verified security professionals can access Claude Mythos 5.1, Opus 5.5, and Sonnet 5.5 with safeguards designed for defensive work. We’re also opening up new tiers to allow for authorized offensive work, like penetration testing and red-teaming. anthropic.com/news/cyber-ver…

Thank you to @UnpromptedAU & @BSidesCbr for inviting me to speak. Being back down under was lovely! You can find the slides for my n-day automated pipeline talk here. I’m at OAIC this week if you want to chat about exploit dev in 2026 and beyond. beautiful.ai/player/-P2q0r-…
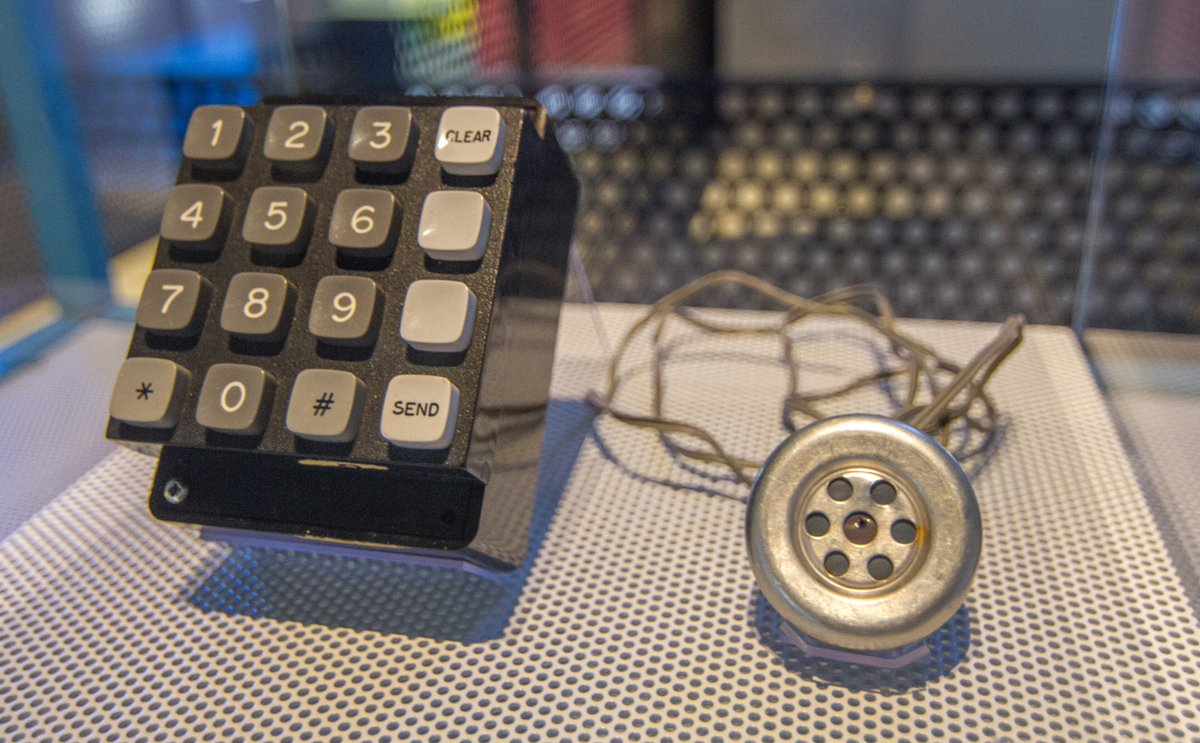
One more Phrack 73 leak for you! Blueboxing Myths and Feelings: a nostalgic dive into phone phreaking’s golden age. archives.phrack.org/dl/73/blueboxi… by @hackerschoice and @GammaTHC
Agree on verification, but I'd push it further. Memory safety is a symptom, not the cause. We got here because of design decisions and trade-offs we made all along, and you can see it in pretty much every recent Linux kernel disclosure. Throwing more tokens at the attack surface won't save us either. Nothing we have today is ready for AI-driven vuln research at this scale, and finding and fixing bugs with AI doesn't change that. What we actually need is redesign and architecture validation with AI, formal methods where we can, and not accepting attack surface at the design phase in the first place. That's just not how we build software today. Patching known bugs doesn't touch the root cause, and hardware has the same problem.
Security will become a larger and larger function in software companies. Security is verification engineering (eg: “my code is probably memory-safe”), as well as capital allocation (“what surface should I throw most tokens at?”) For startups, it’s a challenge and opportunity. As
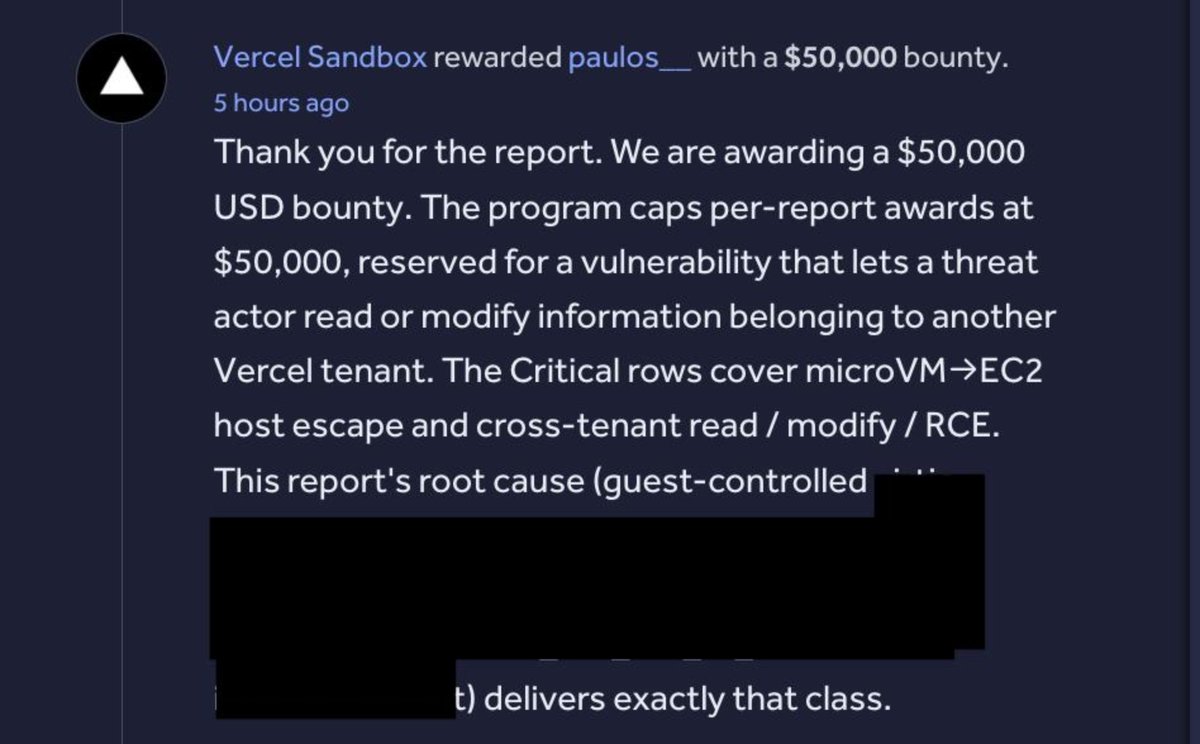
We’ve confirmed a KVM 0day through our Vercel Sandbox bounty program. Affecting the industry’s gold standard solution for Linux virtualization. 2026 is wild! Thankful to Paulos and other researchers helping us make the most secure sandbox for agents. Full writeup coming.
Full VM escape zeroday (guest>host root in industry standard hypervisors)! More soon

It's been one year of our Sprawl meetup! Our 7th event is this Tuesday, with much more planned for later! If you're coming, there's also some @uwu_underground unique tokens to hand out, and Sprawl challenge coins. Website: sprawl.nyc Organized by @withzombies, "OMAR", and I And a huge thanks to all our speakers and hosts! We're always looking for more folks to speak, and event spaces that can host ~100+ people. Let us know if you can help! Below are some new animations I made to play in the background in between talks (quick version, you can see the full thing on the site).

"NVX is an ultra-light micro-VM sandbox for running untrusted workloads with hardware-enforced isolation. It is built on top of OpenVMM and runs Linux as a guest." github.com/microsoft/nvx It looks like it works with Windows Hypervisor Platform (WHVP/WHP) and Linux MSHV.
0xor0ne @0xor0ne
95K Followers 508 Following Cybersecurity | Reverse Engineering | Vulnerability Research | Embedded & Silicon Security | My Tweets, My Opinions :)
Florian Roth ⚡️ @cyb3rops
225K Followers 3K Following Head of Research @nextronsystems #DFIR #YARA #Sigma | detection engineer | creator of @thor_scanner, Aurora, Sigma, LOKI, YARA-Forge | always busy ⌚️🐇 | vi/vim
hasherezade @hasherezade
91K Followers 973 Following Programmer, #malware analyst. Author of #PEbear, #PEsieve, #TinyTracer. Private account. All opinions expressed here are mine only (not of my employer etc)
Ali Hadi | B!n@ry @binaryz0ne
35K Followers 573 Following DFIR and Adversary Simulation | All posts reflect the views and interests of the person behind this account only |
Halvar Flake @halvarflake
48K Followers 3K Following Choose disfavour where obedience does not bring honour. I do math. And was once asked by R. Morris Sr. : "For whom?" @[email protected]
Hex-Rays SA @HexRaysSA
10K Followers 153 Following We are a hi-tech company focusing on binary software analysis - IDA Pro and the Hex-Rays Decompiler. ***Discourse Forum: https://community.hex-rays***
Jiří Vinopal @vinopaljiri
11K Followers 634 Following Security Researcher at @_CPResearch_ All opinions expressed here are mine only. https://t.co/bNWc3k9HwF
Karsten Hahn @struppigel
26K Followers 783 Following MalwareAnalysisForHedgehogs, Principal Malware Researcher at GDATA, he/him 🦔🌈🏳️⚧️
Thomas Roccia 🤘 @fr0gger_
35K Followers 2K Following Founder @SecurityBreakAI AI Security x Threat Intel · Threat Researcher · Creator of #Unprotect & #NOVA · Python 🧡 · Prev @Microsoft @McAfee_Labs
Ange @angealbertini
25K Followers 927 Following Reverse engineer, file formats expert. Corkami, CPS2Shock, PoC||GTFO, Sha1tered, Magika... Security engineer @ Google. He/him.
Saar Amar @AmarSaar
18K Followers 359 Following
Mobile Security @mobilesecurity_
31K Followers 1K Following Mobile Security ✌🏻 #MobileSecurity #AndroidSecurity #iOSsecurity
Richard Johnson @richinseattle
19K Followers 3K Following Computer Security, Reverse Engineering, and Fuzzing; Training & Publications @ https://t.co/mloVP6rPB7; hacking the planet since 1995; Undercurrents BOFH
Łukasz @maldr0id
12K Followers 945 Following Military-grade @Android malware reverse engineer @Google || "Tom Brady of malware strings analysis" - @MalwareTech || Tweets are my own opinions || he/him ✨🌈🦄
Satoshi Tanda @standa_t
8K Followers 397 Following Software security engineer and trainer https://t.co/tenaquooTc
Michael Koczwara @MichalKoczwara
25K Followers 2K Following Threat Researcher/Founder @Intel_Ops_io Threat Intelligence, Adversary Infrastructure Hunting, Curated TI Feed (Coming Soon) https://t.co/VQWaze6gaF
Clandestine @akaclandestine
65K Followers 5K Following | Security | Osint | Threat Research | Opsec | Threat Intelligence | Infosec | Threat Hunting | Humint |
Matthew @embee_research
15K Followers 2K Following Security Researcher, Creating and Sharing Educational Content.

Kasra Arghavani @KSRMMA99
21 Followers 1K Following
nj @nj7wl
38 Followers 276 Following
MrRobot @MrRobot1or0
3 Followers 246 Following
The Skeleton @theskeltondaddy
11 Followers 175 Following
SlyBits @slybits101
2 Followers 114 Following
cardano @mny_crypto
43 Followers 2K Following

Caesar @August4us
3 Followers 201 Following
bug bounty intelligen... @smartaiagents
1 Followers 22 Following AI-powered smart contract security scanner. Trained on 1,032 exact-reconciled Sherlock audit findings. Free pattern search, paid full-repo scans via x402.
Adil @Adilmp25
2 Followers 32 Following
Firef0x @G3suf4l
49 Followers 2K Following
jc @3jc27
25 Followers 459 Following


Fly_Phantom_Fly @Fly_Phantom_Fly
5 Followers 153 Following Android Enthusiast || Reverse Engineer || PhantomThreads

yoker @votersoft
2 Followers 83 Following
Terrence Henry @Ter2ence
139 Followers 609 Following Terry's Lair Pool - TLP #SouthAfrica #Cardano #SPO Covering 4 continents and counting...
Ori @ori52215
0 Followers 18 Following
marian.gheorghe @gheorghe_marian
1 Followers 198 Following
Stefan @st3f4n_r
3 Followers 114 Following

idk @Johnny91436361
1 Followers 169 Following

Nicholas Michael Klos... @showxlate
120 Followers 667 Following Backwards Engineer • ICSA-25-140-11 • Shenaniganist
Cielo Fernandez @Ciel0Fernandez
23 Followers 302 Following
MokkeyDLufffy @MLufffy56633
0 Followers 121 Following

UmVkIERy YWdvbg @Azkto_Gris
9 Followers 209 Following
A a @JasonAin
3 Followers 332 Following
luck day @crow_lahcenid84
0 Followers 92 Following
ricy samuel @RicySamuel74383
0 Followers 4 Following
[email protected] @Hacker4fun_DE
5 Followers 151 Following
Sergey @Sergey77086
0 Followers 53 Following
Exiled @3xi13d
1 Followers 31 Following
Nascar D @xcatcross
0 Followers 12 Following
leep @leeepw
6 Followers 386 Following threw a binary into ida now I’m a professional malware analyst.
The Iridule @The_Iridule
1 Followers 63 Following
Lock @5pinlock
3 Followers 963 Following
parsainfosec @parsainfosec
2 Followers 262 Following
Atharva Bobde @AtharvaBobde
3 Followers 259 Following
Sean McGeever (@seanm... @seanmATed
301 Followers 2K Following University of Edinburgh, Physics and Astronomy, Computing Manager
RightLeft @extremeotami
0 Followers 58 Following
Cailloux @Cailloux968499
22 Followers 3K Following
J Chebu @chebupowerz
0 Followers 125 Following
Pasindu Ravimal @PasinduRavimal
5 Followers 554 Following
Alex Matrosov @matrosov
20K Followers 2K Following Security REsearch @Anthropicai · Breaking & Fixing AI Failure Modes | Founder @binarly_io · @SBOM_Tools · @REhints | Author “Rootkits & Bootkits" (https://t.co/1wd2dfYHY6)

Bill Pollock -- nosta... @billpollock
11K Followers 2K Following Founder, No Starch Press and Hacker Initiative. Views expressed are *entirely* my own. He/him/his Contact our editors at: [email protected]
sergey bratus @sergeybratus
6K Followers 2K Following The cat is the Otocolobus Manul, https://t.co/Xswt7Vp2F1 . Manul is the perfect privacy mascot. All views & opinions are my own & personal.
Rodrigo Branco @bsdaemon
13K Followers 4K Following MTS at does it matter? Advisor of Grsecurity. BYOS Commitee Member of OffensiveCon, Langsec, DistrictCon, Secdev
Trends for United States
You might like