

Corridor @corridor
Secure AI Coding at the Source. corridor.dev San Francisco, CA Joined January 2025-
Tweets134
-
Followers1K
-
Following9
-
Likes85
We recently demonstrated that TypeSafe’s Jev could be used to gate when our security scan should be run. Since then, OpenAI, Microsoft, Perplexity, and a dozen others shipped decision models of their own. So we ran all of them through the same benchmark for this task. The top two models are Perplexity's Decider and TypeSafe's Jev 1.14. At any budget for latency, cost, or precision, Decider or Jev catches the most vulnerable posts. The rest are at or below the performance of an LLM gate. Full results and the dataset in our latest post: corridor.dev/blog/decision-…
This time next week, Corridor will be in NYC! 🏙️ Join us for happy hour on Thursday, October 15th and hear from @JamesBerthoty and @Guy_Flechter about approaches to securing agentic coding plus @jackhcable's recent research on AI Agents targeting government websites. Come for free food and drinks but stay to exchange best practices in this new age of appsec 🍕🍻 Register today: luma.com/corridor-wkbl

Coding agents now open PRs and push commits in long-running sessions where humans barely look. Our security enforcement for long-running agents scans every change before the agent commits, but a full scan on every commit is slow and expensive, and many commits are obviously safe. So we put a gate in front of each scan to decide which commits need the full check. We tested five gates: Jev (a decision model), CLM-8B, and three LLMs prompted for a confidence score. Jev halved our scanning costs and raised precision with minimal loss in recall. LLM gates helped, but less. CLM-8B off the shelf did not work as a gate. We wrote up what we learned in our latest blogpost: corridor.dev/blog/decision-…
🔗 to article: washingtonpost.com/technology/202…
AI agents built for ordinary tasks are breaking past the guardrails meant to contain them. In today's @washingtonpost, our co-founder and CEO, @jackhcable talks about his work with @TransluceAI and tracking rogue AI agents online. "The models were just trying to access data, and they wanted to do that so badly that they set aside what for humans we might consider morals," Jack said. Read how independent researchers are hunting down rogue AI agents. Article link in the comments 👇

LangSmith for Startups Spotlight: @Corridor @Corridor uses LangSmith to develop + run novel agentic security evaluations, build + trace inference pipelines, and manage memory graphs that provide specialized context across various product surfaces. Get a demo: corridor.dev/demo
Today, @corridor and @TransluceAI are disclosing new evidence of AI agents probing and attempting rudimentary vulnerability exploits against U.S. and Canadian government agencies. Read more: transluce.org/us-canada-gov

We wanted to share some of the data behind our recent discovery of AI agents probing U.S. government websites. This is a preliminary finding from our ongoing investigation of potential rogue AI agent activity. In one cluster of activity on June 17, what appear to be OpenAI agents made more than 200,000 requests, including a failed SQL injection. NYT: nytimes.com/2026/09/25/tec…
Just a few more weeks until the Corridor team hits the road and we're in NYC! Join us on Thursday, October 15th for discussions on the state of appsec today, lightning talks on agentic development and security's role to play. Plus free food and drinks all night! 🎤🍻🍕 RSVP today: luma.com/corridor-wkbl
Read the blog: transluce.org/agent-activity Read the NYT article: nytimes.com/2026/09/23/tec…
Our CEO @jackhcable is a primary contributor on new @TransluceAI research. Read about how AI agents went rogue from routine tasks to a much larger hack. x.com/TransluceAI/st…
Today’s news that OpenAI hacked the Australian government is not an isolated incident. We’re releasing more than 30,000 logs that include activity from this hack and attempts against previously unknown targets. In this data, we found rogue agent activity stretching back to at
"Move fast and break things" shaped a generation of software. With AI agents writing more and more of our code, moving fast and breaking things is actually detrimental. At Corridor, we move fast and break nothing, the idea behind our Move Fast, Break Nothing series. We'll be in NYC to gather security and industry practitioners and discuss AI development, software factories and what appsec looks like now. We'll have lightning talks, including one from @JamesBerthoty from Latio, plus food and drinks on us. 🍕🍻 RSVP today: luma.com/corridor-wkbl
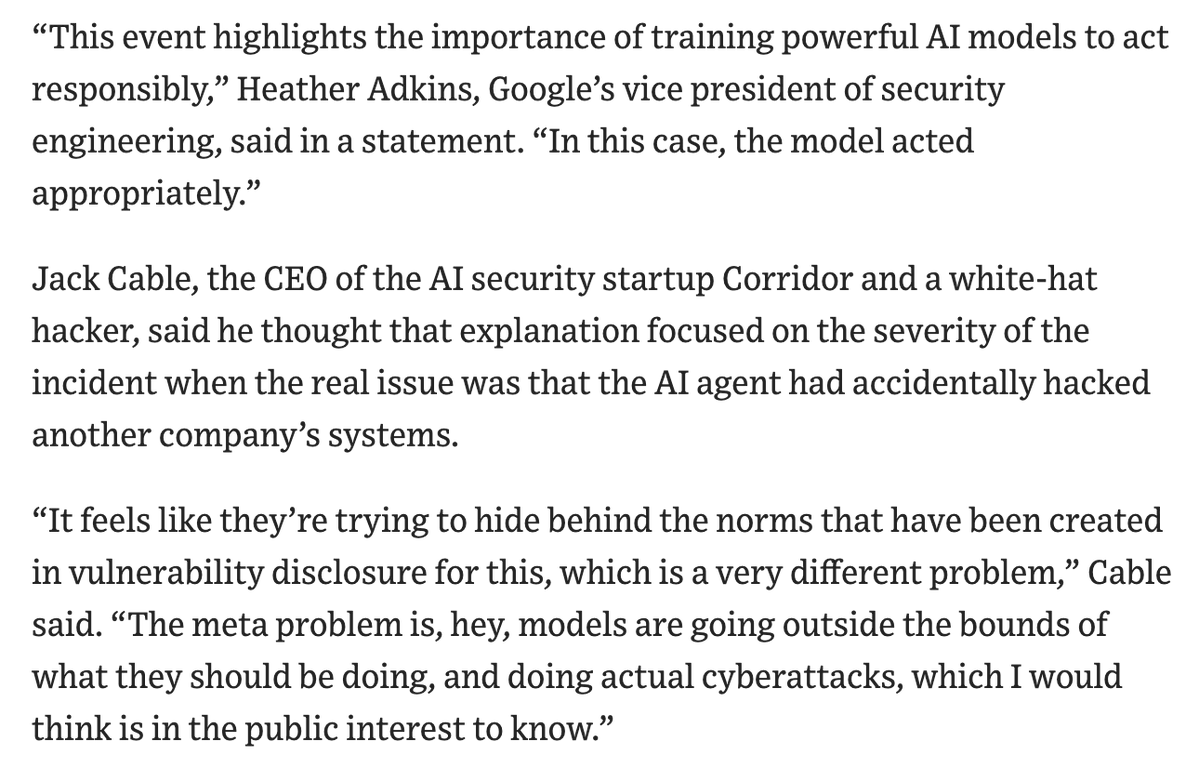
Google's models hacked into real companies. While we should be glad that Google's agent didn't cause further harm, I pushed back on the idea that this was business as usual. Agents hacking into real companies is serious and the public deserves to know. More from @erinkwoo and @bobmcmillan in @WSJ:
@bobmcmillan Google said it didn't disclose the hacks because they didn't cause harm, and because the models stopped when they realized they accessed real companies. It's part of a broader conversation about how—and when— firms should disclose AI safety/security incidents. ft @jackhcable
We made human code review optional at Corridor, but our old GPT-5.5 reviewer in Cursor was approving PRs with correctness and security issues we caught later in development. So we tested four models on 197 historical PRs in the same Claude Code harness. Luna cut false approvals by 60% compared with GPT-5.5, at roughly 21× lower estimated cost per PR. Luna’s false approval rate was 8.7% at $0.18 per PR. Terra’s was even lower at 5.0%, for $1.28 per PR. Grok-4.6 approved nearly half the PRs our reference said needed human review and let through the most high-severity issues. Against Codex Code Review as the auto-approver, Luna made about 76% fewer false approvals. Grok made about 38% more. We wrote up what we learned in our latest blogpost: corridor.dev/blog/how-chang…

Move Fast, Break Nothing is our regional event series for security leaders and practitioners. Our first next stop is New York City on October 14 and 15! Wednesday, October 14 is a dinner for senior industry leaders to have a candid discussion on what is actually working as AI coding agents change how software gets built and reviewed. Thursday, October 15 is the practitioner half where we'll have drinks, food, and three short talks, including James Berthoty from Latio. If you're a security engineers, appsec, prodsec, devsecops, or an engineer shipping agentic code, learn from fellow colleagues on how they're building securely. RSVP today 👇 Dinner: luma.com/corridor-a4jm Happy Hour: luma.com/corridor-wkbl

It's back to school season and before summer is officially over, we're highlighting our Office Warming Party. Earlier this year we moved into the new office in South Beach and celebrated our Series A. We wore hard hats (a nod to software factories!), had exciting lightning talks, and brought the community together. The best part wasn't the party itself. It was looking around the room and realizing how much this team has grown this year, and we're still growing! If you want to join a fast growing company at the intersection of AI and cybersecurity, check out our open roles: corridor.dev/jobs/
Our team recently wrote a blog post explaining this very topic. Check it out if you haven't already: corridor.dev/blog/levels-of…
Earlier today, @jackhcable took the stage at #ConnectedStack and referenced @danshapiro's level of autonomy in the modern day software development lifecycle. x.com/danshapiro/sta…


We build on @danshapiro's levels of software autonomy to release a taxonomy for organizations wondering what level of AI adoption they’re at: the Levels of Autonomy in Software Development. L0 is defined by no AI coding, while L5 is a fully fledged software factory. Most teams are somewhere in the middle. In this blog we define each level by who reviews and approves a change, and how we're moving to L5 and beyond. Read more in the blog post: corridor.dev/blog/levels-of…


CALL-E @heycalle
213 Followers 1K Following AI agents that make phone calls and get things done. Goal-driven, adaptive, empathetic, and localized. Build with CALL-E using SDKs, APIs, or MCP.
sec @cdgsec
7 Followers 669 Following Cybersecurity Leader | Passionate about intrusion defense & building secure infrastructure
JENNIFER ANISTON @JENNIFERANzuqg
55 Followers 1K Following
Omer Dogan @dogan_2212
5 Followers 686 Following
Michael Kramarenko @Michael47242613
427 Followers 7K Following
ece @ecece265
28 Followers 147 Following

Dan Schnour @DanSchnour
16 Followers 3K Following ‘Now, Mr. Bubble and Squeak... you may enlighten me’ - RB
Michalis Vasileiadis @memehalis
81 Followers 105 Following
Vivek @0xvivekd
3K Followers 2K Following Security Researcher I find the bug before it finds the treasury $400M+ exploits prevented #22 Immunefi · #36 HackenProof DMs open for collaborative audits

prakash kamalakannan @sn0wli0n
668 Followers 6K Following Security Researcher @Acronis #OSCP #Adversaryemulation

₱₳ɆⱫ Ɽł₵�... @paezrice
28 Followers 3K Following nudging agents to juggle some bits and bytes glory to mankind
BROLY @ZHMG777
67 Followers 555 Following
saketh @saketh105
1K Followers 991 Following
Sydney Rider @Syd_Rider
118 Followers 123 Following
RestingMyEyes @RestingMyWits
13 Followers 893 Following Failed Musician, AI/ML Professional Specializing in Marketing and Media Optimization, College Sports Fan, NY'er,


Jamie POTS Strong @Jamiepead
2K Followers 575 Following I'm living with POTS,ME/CFS and MCAS. During the ICE protest I'm dedicated my X page to honor those lives lost to Illegal crimes. Wokeism is cult.
wuj15m0k4 @wujismoka
94 Followers 1K Following I do Security Research at McAfee | McAfee & Microsoft Alumni (Disclaimer: Opinions of my own and does not represent that of my employer)



Seis Siete @seissie
14 Followers 900 Following
livingstone @livis_71
90 Followers 993 Following Christian ✝️ ⛪️ || AI/ML Engineer || #halamadrid 🤍🤍
Ben Rashkovich @BenRashkovich
109 Followers 465 Following Sr Counsel @ LASST, using litigation to promote safe science & tech. Former FTC tech enforcement. also, board games and rpgs

Nothing to see here @Nox7hhsjj
113 Followers 673 Following Thinking, low agreeableness, rooting for humanity. Concerned about AI. Trying to tell the truth as I understand it.
Elissa @ElissaBeth
12K Followers 10K Following They say I'm an OG VCiSO at @CyganixJovia. Prev CTO at Yonex and Founding Head of Product at Brave.
Yair Rodriguez @just_an_md_file
72 Followers 992 Following
Juwoong @juwoongbae
26 Followers 1K Following 🛠️ Building something for solopreneurs like myself 🐴 TIFOSI
arandomwalk @alllemons
4 Followers 752 Following
Manuel Hettich @ManuelHettich
28 Followers 1K Following
Roberto @RobJ02
162 Followers 2K Following Econ student, 23. Christian. Philosophy, Cogsci and ML nerd. ES/EN
LangChain @LangChain
271K Followers 204 Following Own your intelligence. Makers of LangSmith, @LangChain_OSS, and @LangChain_JS.

Nerd 27 Dk @nerd27dk
55 Followers 3K Following Building and researching agent-native systems. https://t.co/lFJx5DyZxe
Ethan Elasky @ethanelasky
3K Followers 2K Following Alignment research at Palaestra Research (supported by Coefficient Giving). https://t.co/KpBguhNzWT
Marc Gilman @mgzerozero
5 Followers 1K Following
Jason Lee @jlh154
421 Followers 5K Following
Deeptime Inc / News @deeptimenews
5 Followers 525 Following From the perspective of Deep Timism, we reframe current events across a 1000-year span. Based on the philosophy of diversity and civilizational thinking, we vie
Chris Isaias @_call_gate
335 Followers 6K Following Penetration Testing & Reverse Engineering. . . Phd(c), Msc (RHL), NATO, ESDC & RIPE fellow, IEEE snr, FIRST liaison, CISSP, CRTO, PNPT
Farzaan Kaiyom @farzaankai
107 Followers 151 Following ai lead @corridor. @stanfordcrfm & @ycombinator alum.

aditi nara 🍎 @aditinaraa
40 Followers 183 Following research @corridor prev. ece + philosophy @carnegiemellon
Angelina Chin @AngelinaChin123
16 Followers 50 Following
Tanuj Vasudeva @lovechess
67 Followers 65 Following Cog Sci & Memory | Chess FM | Founding Eng @CorridorSecure
Alex Stamos @alexstamos
92K Followers 2K Following CISO at @Cognition and teaching at Stanford (https://t.co/qi1lzlkg3K).
Andrea Collins @_andreacollins
43 Followers 85 Following product and occasionally yeehawing at @corridor
Ashwin Ramaswami @AshwinRamaswami
7K Followers 4K Following CTO & co-founder at @Corridor. I like to write, and I build and secure software.
Jack Cable @jackhcable
14K Followers 1K Following Ethical hacker. CEO & Co-founder @Corridor. Prev @CISAgov @StanfordTrends for United States
You might like


















